ISS Forensics
EN/ΕΛ

INDEPENDENT DIGITAL FORENSICS · CYPRUS

Digital evidence.
Clear answers.

When the facts matter, the details matter. Independent examination of digital evidence, clear reporting and expert testimony.

For lawyers, businesses & individuals.Preserve the source. Understand the evidence.
Documented handlingEvidence-led analysisIndependent reporting

OUR EXPERTISE

Complex evidence.
A clear way forward.

Every matter starts with a question. We identify the relevant digital sources, examine what they contain and explain what the findings support.

Our examinations are independent and objective. We report material findings whether they support or challenge the position under examination. We explain what the digital evidence supports, the limitations that apply and what cannot be established.

04 — 09

Digital evidence examinations

From the original source to findings you can understand.

04

Computer & mobile forensics

Preserve the source. Examine the available data.

Authorised forensic acquisition, preservation and examination of computers, mobile devices and storage media. We extract relevant data and recover deleted material where technically possible, recording the methods used and the limits of the available evidence.

Devices · Forensic copies · Data recovery
05

Malware & exploit forensics

Assess suspected compromise and its relevance to the evidence.

Forensic examination of phones, computers and available email and cloud records for indications of malware, spyware, stalkerware, exploitation or unauthorised access. We correlate findings with disputed activity, including claims that malware was responsible. We assess what the evidence supports about timing and actions, distinguish potential capabilities from documented activity, and explain the limits of attributing actions to a person.

Malware & spyware · Exploitation traces · Email & cloud access
06

Messages & screenshots

Understand the conversation in context.

Examination of messages and screenshots against available original records. We assess chronology, context and completeness, distinguishing what is visible from what the source data can establish about origin and attribution.

Messages · Source records · Context
07

Electronic documents

Trace the available document history.

Examination of document metadata, versions and indications of editing or transfer. We correlate file properties with available device records and explain what can be established about changes, timing and authorship.

Documents · Metadata · Versions
08

CCTV & alarm systems

Reconstruct the sequence of events.

Preservation and examination of CCTV recordings, native exports and available alarm or monitoring logs. We assess recording continuity, clock differences and event sequences, correlating video with activation, arming, disarming and response records where available.

CCTV · Alarm logs · Event timelines
09

Websites & online evidence

Preserve content before it changes.

Documented capture and preservation of available websites, online publications, images and files. We record sources and collection times, preserve the collected material and compare it with supplied originals for use in disputes about published or reused content.

Websites · Online publications · Content comparison
10 — 11

Specialist investigations & independent review

Focused examination of the events, records and conclusions in dispute.

10

Corporate data transfer

Investigate what happened to company information.

Technical investigation of suspected copying, disclosure, retention or deletion of business information, including matters involving employees or former collaborators. We correlate file activity, external media and available company-system records to identify events supported by the evidence and explain their context.

Company data · Internal investigations · File transfers
11

Independent forensic report review

Test the basis of the conclusions.

Independent review of another forensic report, its methods, search coverage and evidential reasoning. We compare material findings with available source data, consider alternative explanations and identify unsupported conclusions or limitations.

Expert reports · Methods · Source support

THE APPROACH

A traceable process.
From source to finding.

A defensible finding needs a traceable basis. We document the acquisition, tools, procedures and limitations so that the examination and its conclusions can be independently assessed.

  1. 01

    Define

    Agree the authority, questions, relevant sources and scope with you and your legal adviser before examination begins.

  2. 02

    Preserve

    Document receipt, handling and transfers. Preserve source material and use verified forensic copies or appropriate exports wherever practicable. Record acquisition methods and appropriate integrity checks, including cryptographic hashes where applicable.

  3. 03

    Examine

    Check material findings against their sources. Correlate records and timelines, test alternative explanations and document examination coverage.

  4. 04

    Explain

    Report findings objectively. Distinguish observations, interpretation and limitations, with references that allow the reasoning to be followed.

A keyword result or a device event needs context. Our conclusions reflect the available evidence and the limits of the examination.

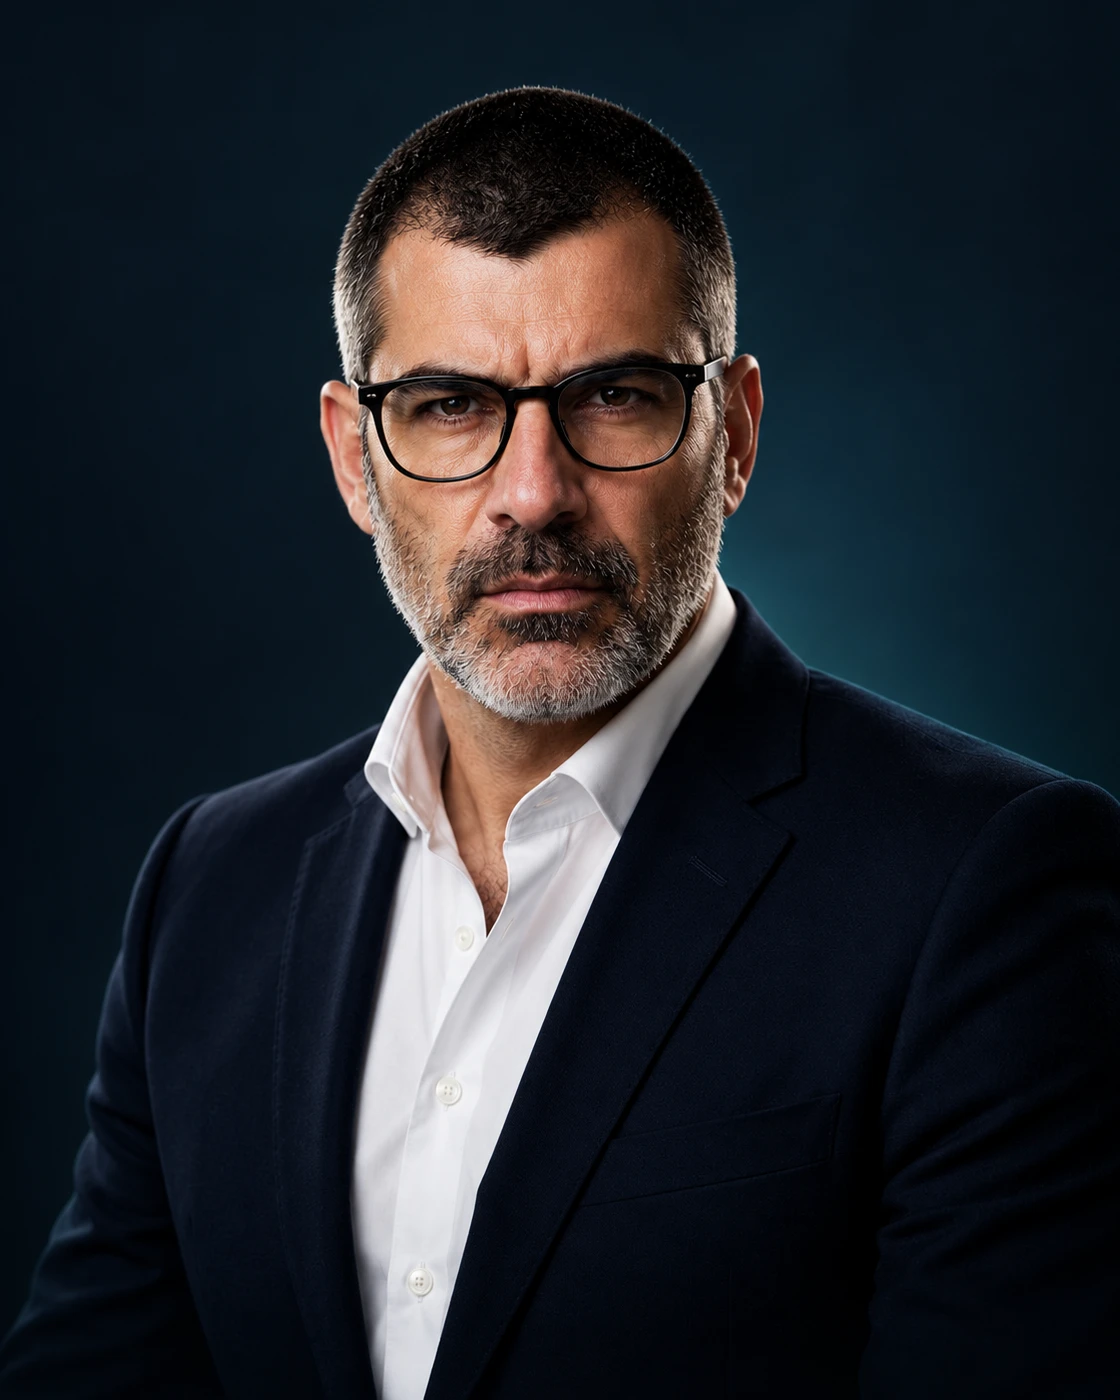
ALEXIS MAVROS

Alexis Mavros — stylized portrait

Qualifications & certifications

  • University College Dublin (UCD)MSc

    Digital Investigations & Forensic Computing

    University College Dublin, Ireland

  • IACIS — Certified Forensic Computer ExaminerCFCE

    Certified Forensic Computer Examiner

    The International Association of Computer Investigative Specialists (IACIS)

IN THE MEDIA

Articles and interviews

Articles and commentary by Alexis Mavros on digital evidence.

AlphaNewsOpinionGreek

Υπόθεση Μαζωνάκη: Η σημασία των καταγραφών των ιατρικών συσκευών και πώς μπορούν να συμβάλλουν στην αποκάλυψη της αλήθειας

Άρθρο του Αλέξη Μαύρου για τη συνεξέταση ψηφιακών τεκμηρίων και καταγραφών ιατρικών συσκευών.

Read ↗
ΠολίτηςRadioGreek

«Γίνονταν και γίνονται παρακολουθήσεις στην Κύπρο»: Το «βαλιτσάκι» και άλλες δύο μέθοδοι που χρησιμοποιούνται – Τρόποι προστασίας (ηχητικό)

Ραδιοφωνική παρέμβαση του Αλέξη Μαύρου για την παρακολούθηση κινητών και την προστασία των χρηστών.

Listen ↗
Ant1 Live News - ΚύπροςTVGreek

Οι βασικότερες μορφές παρακολούθησης - Τρόπος προστασίας πολιτών

Watch ↗
ΠολίτηςOpinionGreek

«Ποιος έστειλε πραγματικά το email; Η απάντηση κρύβεται στα ψηφιακά ίχνη» του Αλέξη Μαύρου

Άρθρο του Αλέξη Μαύρου για την τεχνική διερεύνηση της προέλευσης και της αυθεντικότητας email.

Read ↗
AlphaNewsArticleGreek

Ψεύτικα e-mail: Έτσι έστειλαν στην Αννίτα τα απειλητικά μηνύματα, πώς να τα αναγνωρίσετε

Δημοσιογραφική αναφορά σε παρέμβαση του Αλέξη Μαύρου για τον έλεγχο ηλεκτρονικών μηνυμάτων και την ψηφιακή προστασία.

Read ↗
ΠολίτηςOpinionGreek

Όταν τα ψηφιακά ίχνη μιλούν πιο δυνατά από τους ισχυρισμούς

Read ↗
All appearances (13)
AlphaNewsOpinionGreek

Το ένταλμα έρευνας και τα όρια της κρατικής εξουσίας στην ψηφιακή εποχή

Άρθρο του Αλέξη Μαύρου για την αναλογικότητα και τα όρια πρόσβασης σε ηλεκτρονικά δεδομένα κατά την εκτέλεση ενταλμάτων έρευνας.

Read ↗
ΠολίτηςInterviewGreek

Αλέξης Μαύρος: Τα fake sms δεν αντέχουν τον δικανικό έλεγχο

Συνέντευξη του Αλέξη Μαύρου στην Κατερίνα Ηλιάδη για την αξιολόγηση ψηφιακών τεκμηρίων και τις δυνατότητες ανάκτησης δεδομένων.

Read ↗
AlphaNews LiveInterviewGreek

Ο Αλέξης Μαύρος για την αυθεντικότητα μηνυμάτων και στοιχείων | AlphaNews Live

Watch ↗
Ant1 Live News - ΚύπροςInterviewGreek

Δικανικός επιστήμονας Αλέξης Μαύρος για υπόθεση «Σάντη»

Watch ↗
AlphaNewsArticleGreek

Ιδού το επτασέλιδο πόρισμα του εμπειρογνώμονα Μαύρου για τα κινητά Παπαδάκη

Δημοσίευμα για το πόρισμα του Αλέξη Μαύρου σχετικά με την εξέταση κινητών τηλεφώνων του Δημήτρη Παπαδάκη.

Read ↗
AlphaNews LiveTVGreek

Αλέξης Μαύρος: Η υπόθεση Σάντη και ο ρόλος των ψηφιακών πραγματογνωμόνων

Watch ↗
AlphaNews LiveTVGreek

Ισχυρισμοί Δρουσιώτη: Θύμα πλεκτάνης δηλώνει ο Παπαδάκης | AlphaNews Live

Watch ↗

QUESTIONS WE HELP ANSWER

Start with the question.
Follow the evidence.

Illustrative examples of the questions an examination may address. The available sources determine what can be established.

BUSINESS & EMPLOYMENT

Were company files transferred?

Correlate file activity, external-device traces and other available records to assess a suspected transfer.

COMMUNICATIONS

Does the message record tell the whole story?

Examine available messages, metadata and source context to assess consistency, chronology and completeness.

INDEPENDENT REVIEW

Is the conclusion supported?

Review the underlying artefacts and analysis, considering attribution limits and plausible alternative explanations.

FOR LAWYERS & CLIENTS

A clear brief.
A useful examination.

Start with the issue that needs a technical answer. We can then identify the material, scope and next steps relevant to your case.

For your first conversation

  1. 01

    The question

    Briefly describe what is disputed or needs to be established, and whether a lawyer is handling the matter.

  2. 02

    The available sources

    Tell us which devices, accounts, recordings, reports or forensic copies exist, who holds them and the relevant period.

  3. 03

    The deadline

    Mention any hearing date, disclosure deadline or risk that relevant data may be lost.

Keep the initial enquiry general. Contact us before sending evidence, passwords or confidential case documents so that an appropriate transfer method can be agreed.

Discuss your case with Alexis

Before you instruct us

Can you review a report by the police or another expert?

Yes. An initial technical review may be possible from the report and its exhibits. Checking the underlying findings may also require forensic copies, extraction files, source devices or other disclosed data. We identify what is available, what is missing and how that affects the review.

Are screenshots enough to examine a conversation?

Screenshots can help identify the disputed material, but may omit surrounding messages, source information and metadata. Where available and lawfully accessible, we compare them with relevant device, backup or account records. We explain the limits of what can be verified; an account or device record alone does not necessarily identify the person responsible.

Can you confirm my phone is not infected?

We can examine a device for known malware, spyware and signs of compromise using the methods, indicators and source data available for the examination. If no such indicators are found, that conclusion is limited to the material and methods examined. It is not a guarantee that the device is free of malware or was never compromised. We explain the scope, coverage and limitations in the report.

What does a forensic report include?

The report addresses the agreed questions and identifies the material examined, methods, significant findings, supporting references and limitations. It separates observations from technical interpretation. Timelines and exhibits may accompany the report where relevant. A discussion with your lawyer and court testimony can be arranged where required and agreed.

What should I do with a device that may contain evidence?

Contact us promptly for advice specific to the device and its current state. Avoid unnecessary use, resets, updates, deletions and attempts to recover data yourself. Seek guidance before changing its power or network state, and record who has handled it. The appropriate preservation steps depend on the source and circumstances.

How are cost and timing assessed?

They depend on the questions, amount and condition of the material, access requirements and examination needed. We discuss the proposed scope, timing and fees before the examination starts. Tell us about relevant deadlines at first contact so that feasibility can be assessed.

What if the findings do not support my position?

Our technical assessment remains independent. We report material findings that support or challenge the position being examined, explain uncertainty and distinguish the evidence from assumptions. Your lawyer assesses the legal significance of the findings.

LET’S START WITH YOUR QUESTION

Make sense of
your digital evidence.

Tell us briefly about the matter and the digital sources involved. We can discuss the appropriate next step and the proposed scope.

Based in Cyprus · English & Greek

WHATSAPPChat on WhatsAppEMAILmavros@iss.com.cyCALL+357 95 111555

Keep your initial enquiry general. Evidence transfer can be arranged after authority and scope are agreed.

WhatsApp